Correct Drag-and-Drop Sequence:
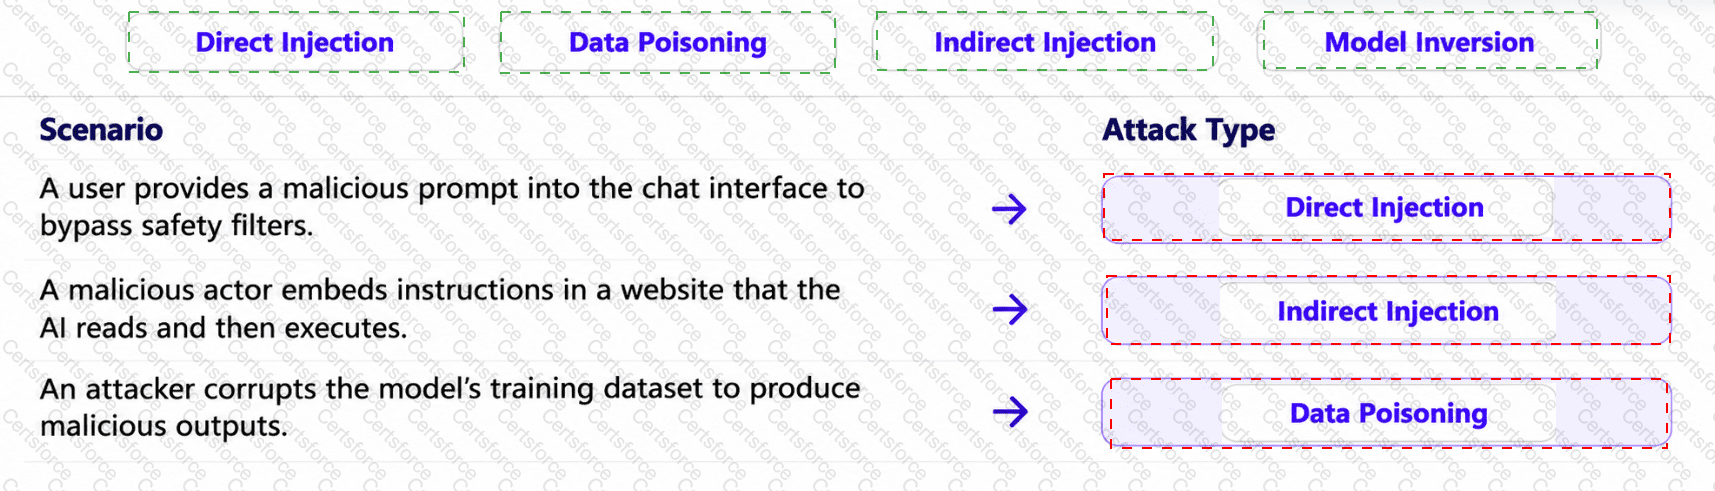
Direct Injection
Indirect Injection
Data Poisoning
AI systems face several security threats that exploit different stages of model operation, including inference, external information retrieval, and training. The three scenarios demonstrate distinct attack mechanisms.
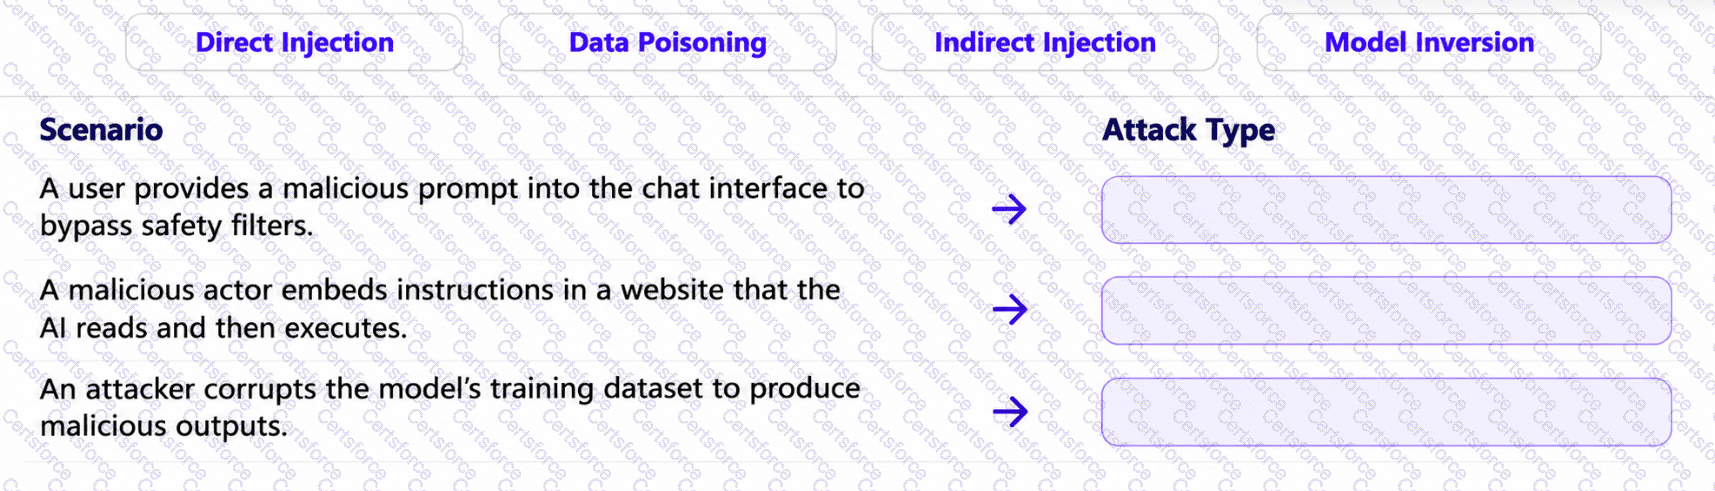
1. Direct Injection: Direct prompt injection occurs when an attacker submits malicious instructions directly through an AI application's input interface. In this scenario, the attacker attempts to bypass safety filters by manipulating the model's behavior through a crafted prompt. Direct injection commonly includes jailbreaking attempts and instructions designed to override established restrictions.
2. Indirect Injection: Indirect prompt injection occurs when malicious instructions are embedded in external content that an AI system subsequently processes. For example, an attacker may place hidden instructions inside a webpage, document, or API response. If the AI treats these instructions as authoritative, it may perform unintended operations.
3. Data Poisoning: Data poisoning involves deliberately manipulating training datasets to influence future model behavior. Attackers may introduce misleading examples, corrupted labels, or malicious records, causing the model to generate inaccurate or harmful outputs.
Model Inversion (Unused): Model inversion attacks attempt to infer or reconstruct sensitive information about training data from a model's outputs or other observable information.
These distinctions are essential for implementing appropriate AI security controls, including input validation, data integrity protection, access restrictions, and continuous monitoring.
OWASP Gen AI Security Project+1
Specific Cisco AITECH Course Guide References:
Generative AI Security and Privacy Fundamentals
Prompt Engineering for Technical Precision
Exam Objective 2.3: Describe prompt injection attack types
Exam Objective 3.3: Explain AI-specific security threats and risks
Exam Objective 3.4: AI governance and risk management
===================


Submit